

Free 365 Days Exam Updates CCST-Networking dumps with test Engine Practice
Updated Verified CCST-Networking dumps Q&As - 100% Pass Guaranteed
Cisco CCST-Networking Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 21
Which command will display the following output?
- A. show mac-address-table
- B. show ip interface
- C. show inventory
- D. show cdp neighbor
Answer: D
Explanation:
The command that will display the output provided, which includes capability codes, local interface details, device IDs, hold times, and platform port ID capabilities, is the show cdp neighbor command. This command is used in Cisco devices to display current information about neighboring devices detected by Cisco Discovery Protocol (CDP), which includes details such as the interface through which the neighbor is connected, the type of device, and the port ID of the device1.
References :=
*Cisco - show cdp neighbors
The provided output is from the Cisco Discovery Protocol (CDP) neighbor table. The show cdp neighbor command displays information about directly connected Cisco devices, including Device ID, Local Interface, Holdtime, Capability, Platform, and Port ID.
*A. show mac-address-table: Displays the MAC address table on the switch.
*C. show inventory: Displays information about the hardware inventory of the device.
*D. show ip interface: Displays IP interface status and configuration.
Thus, the correct answer is B. show cdp neighbor.
References :=
*Cisco CDP Neighbor Command
*Understanding CDP
NEW QUESTION # 22
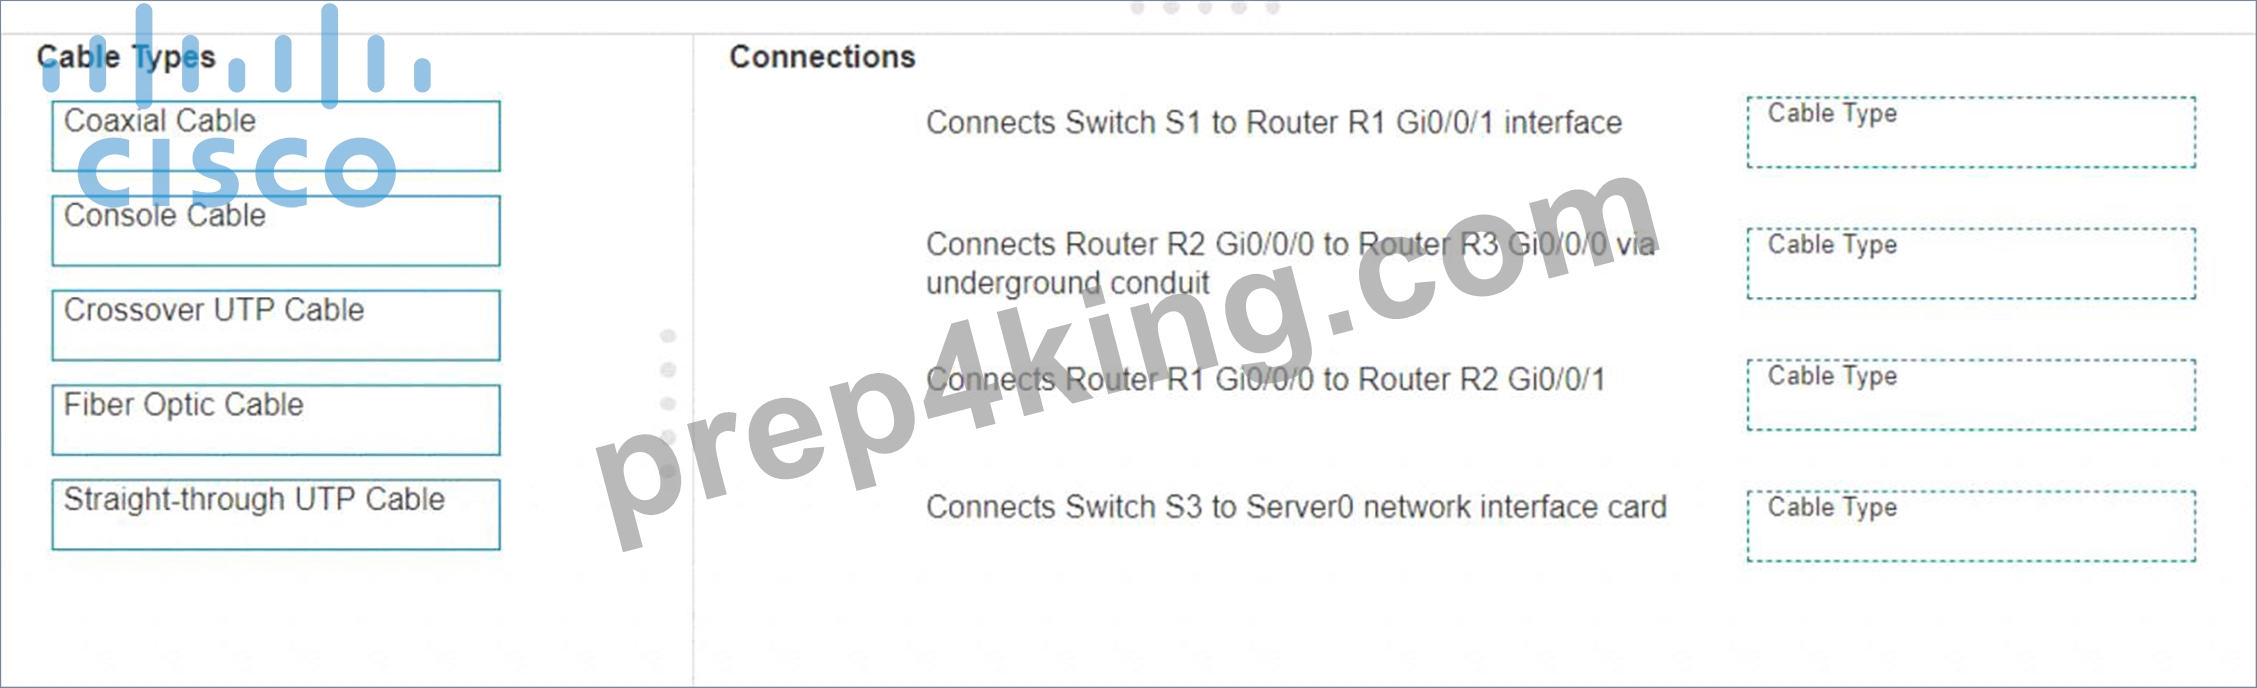
Examine the connections shown in the following image. Move the cable types on the right to the appropriate connection description on the left. You may use each cable type more than once or not at all.
Answer:
Explanation:
Explanation:
Based on the image description provided, here are the cable types matched with the appropriate connection descriptions:
Connects Switch S1 to Router R1 Gi0/0/1 interfaceCable Type: = Straight-through UTP Cable Connects Router R2 Gi0/0/0 to Router R3 Gi0/0/0 via underground conduitCable Type: = Fiber Optic Cable Connects Router R1 Gi0/0/0 to Router R2 Gi0/0/1Cable Type: = Crossover UTP Cable Connects Switch S3 to Server0 network interface cardCable Type: = Straight-through UTP Cable The choices are based on standard networking practices where:
* Straight-through UTP cablesare typically used to connect a switch to a router or a network interface card.
* Fiber optic cablesare ideal for long-distance, high-speed data transmission, such as connections through an underground conduit.
* Crossover UTP cablesare used to connect similar devices, such as router-to-router connections.
These matches are consistent with the color-coded cables in the image: green for switch connections, yellow for router-to-router connections within the same rack, and blue for inter-rack connections. The use of these cables follows the Ethernet cabling standards.
* Connects Switch S1 to Router R1 Gi0/0/1 interface:
* Cable Type: Straight-through UTP Cable
* Explanation: A straight-through UTP cable is typically used to connect different types of devices, such as a switch to a router.
* Connects Router R2 Gi0/0/0 to Router R3 Gi0/0/0 via underground conduit:
* Cable Type: Fiber Optic Cable
* Explanation: Fiber optic cables are used for long-distance connections, such as those through an underground conduit between buildings.
* Connects Router R1 Gi0/0/0 to Router R2 Gi0/0/1:
* Cable Type: Crossover UTP Cable
* Explanation: A crossover UTP cable is typically used to connect similar devices directly, such as router to router connections.
* Connects Switch S3 to Server0 network interface card:
* Cable Type: Straight-through UTP Cable
* Explanation: A straight-through UTP cable is typically used to connect a switch to an end device, such as a server.
* Straight-through UTP Cable: Used to connect different devices (e.g., switch to router, switch to server).
* Crossover UTP Cable: Used to connect similar devices directly (e.g., router to router, switch to switch).
* Fiber Optic Cable: Used for long-distance and high-speed connections, often between buildings or data centers.
References:
* Network Cable Types and Uses: Cisco Network Cables
* Understanding Ethernet Cabling: Ethernet Cable Guide
NEW QUESTION # 23
Move each protocol from the list on the left to its correct example on the right.
Answer:
Explanation: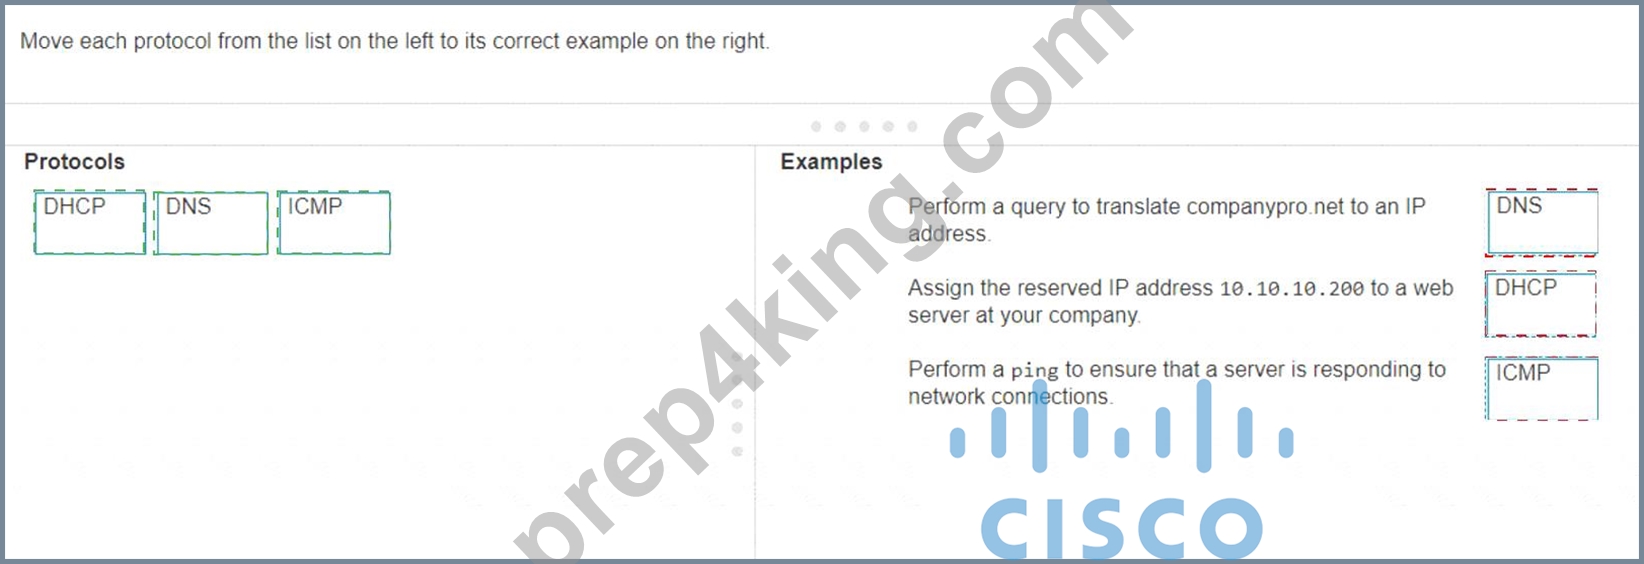
Explanation:
The correct matching of the protocols to their examples is as follows:
* DHCP: Assign the reserved IP address 10.10.10.200 to a web server at your company.
* DNS: Perform a query to translate companypro.net to an IP address.
* ICMP: Perform a ping to ensure that a server is responding to network connections.
Here's how each protocol corresponds to its example:
* DHCP (Dynamic Host Configuration Protocol)is used to assign IP addresses to devices on a network.
In this case, DHCP would be used to assign the reserved IP address 10.10.10.200 to a web server.
* DNS (Domain Name System)is used to translate domain names into IP addresses. Therefore, to translate companypro.net to an IP address, DNS would be utilized.
* ICMP (Internet Control Message Protocol)is used for sending error messages and operational
* information indicating success or failure when communicating with another IP address. An example of this is using the ping command to check if a server is responding to network connections.
These protocols are essential for the smooth operation of networks and the internet.
* Perform a query to translate companypro.net to an IP address.
* DNS (Domain Name System): DNS is used to resolve domain names to IP addresses.
* Assign the reserved IP address 10.10.10.200 to a web server at your company.
* DHCP (Dynamic Host Configuration Protocol): DHCP is used to assign IP addresses to devices on a network.
* Perform a ping to ensure that a server is responding to network connections.
* ICMP (Internet Control Message Protocol): ICMP is used by network devices to send error messages and operational information, and it is the protocol used by the ping command.
* DNS (Domain Name System): DNS translates human-friendly domain names like "companypro.net" into IP addresses that computers use to identify each other on the network.
* DHCP (Dynamic Host Configuration Protocol): DHCP automatically assigns IP addresses to devices on a network, ensuring that no two devices have the same IP address.
* ICMP (Internet Control Message Protocol): ICMP is used for diagnostic or control purposes, and the ping command uses ICMP to test the reachability of a host on an IP network.
References:
* DNS Basics: What is DNS?
* DHCP Overview: What is DHCP?
* ICMP and Ping: Understanding ICMP
NEW QUESTION # 24
What is the purpose of assigning an IP address to the management VLAN interface on a Layer 2 switch?
- A. To enable the switch to provide DHCP services to other switches in the network
- B. To enable the switch to act as a default gateway for the attached devices
- C. To enable access to the CLI on the switch through Telnet or SSH
- D. To enable the switch to resolve URLs for the attached the devices
Answer: C
Explanation:
The primary purpose of assigning an IP address to the management VLAN interface on a Layer 2 switch is to facilitate remote management of the switch. By configuring an IP address on the management VLAN, network administrators can access the switch's Command Line Interface (CLI) remotely using protocols such as Telnet or Secure Shell (SSH). This allows for convenient configuration changes, monitoring, and troubleshooting without needing physical access to the switch1.
References :=
*Understanding the Management VLAN
*Cisco - VLAN Configuration Guide
*Remote Management of Switches
Assigning an IP address to the management VLAN interface (often the VLAN 1 interface by default) on a Layer 2 switch allows network administrators to remotely manage the switch using protocols such as Telnet or SSH. This IP address does not affect the switch's ability to route traffic between VLANs but provides a means to access and configure the switch through its Command Line Interface (CLI).
*A: The switch does not act as a default gateway; this is typically a function of a Layer 3 device like a router.
*B: The switch does not resolve URLs; this is typically a function of DNS servers.
*C: The switch can relay DHCP requests but does not typically provide DHCP services itself; this is usually done by a dedicated DHCP server or router.
Thus, the correct answer is D. To enable access to the CLI on the switch through Telnet or SSH.
References :=
*Cisco VLAN Management Overview
*Cisco Catalyst Switch Management
NEW QUESTION # 25
Move each cloud computing service model from the list on the left to the correct example on the right Note: You will receive partial credit for each correct answer.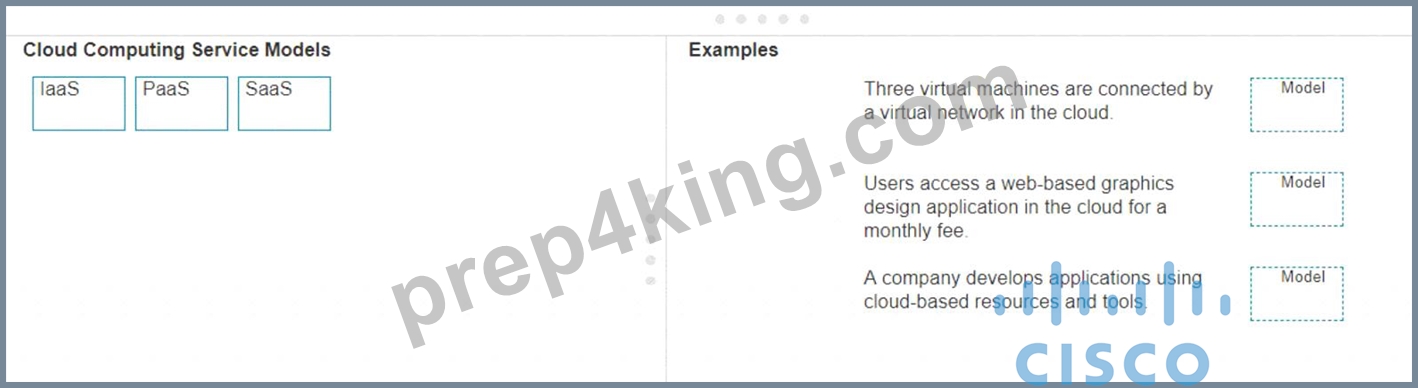
Answer:
Explanation:
Explanation:
* Three virtual machines are connected by a virtual network in the cloud.
* Model: IaaS (Infrastructure as a Service)
* Explanation: IaaS provides virtualized computing resources over the internet, including virtual machines, storage, and networks.
* Users access a web-based graphics design application in the cloud for a monthly fee.
* Model: SaaS (Software as a Service)
* Explanation: SaaS delivers software applications over the internet, typically on a subscription basis, accessible via a web browser.
* A company develops applications using cloud-based resources and tools.
* Model: PaaS (Platform as a Service)
* Explanation: PaaS provides a platform allowing customers to develop, run, and manage applications without dealing with the infrastructure.
* IaaS (Infrastructure as a Service): Provides virtualized hardware resources that customers can use to build their own computing environments.
* PaaS (Platform as a Service): Offers a platform with tools and services to develop, test, and deploy applications.
* SaaS (Software as a Service): Delivers fully functional applications over the internet that users can access and use without managing the underlying infrastructure.
References:
* Cloud Service Models: Understanding IaaS, PaaS, SaaS
* NIST Definition of Cloud Computing:NIST Cloud Computing
NEW QUESTION # 26
A Cisco PoE switch is shown in the following image. Which type of port will provide both data connectivity and power to an IP phone?
- A. Ports identified with number 7
- B. Port identified with number 2
- C. Ports identified with number 6
- D. Ports identified with numbers 3 and 4
Answer: C
Explanation:
In the provided image of the Cisco PoE switch, the ports identified with number 6 are the standard RJ-45 Ethernet ports typically found on switches that provide both data connectivity and Power over Ethernet (PoE).
PoE ports are designed to supply power to devices such as IP phones, wireless access points, and other PoE-enabled devices directly through the Ethernet cable.
Ports:
*2: Console port (for management and configuration)
*3 and 4: Specific function ports (often for management)
*6: RJ-45 Ethernet ports (capable of providing PoE)
*7: SFP ports (for fiber connections, typically do not provide PoE)
Thus, the correct answer is C. Ports identified with number 6.
References :=
*Cisco Catalyst 2960-L Series Switches Data Sheet
*Cisco PoE Overview
NEW QUESTION # 27
An app on a user's computer is having problems downloading data. The app uses the following URL to download data:
https://www.companypro.net:7100/api
You need to use Wireshark to capture packets sent to and received from that URL.
Which Wireshark filter options would you use to filter the results? Complete the command by selecting the correct option from each drop-down list.
Note: You will receive partial credit for each correct selection.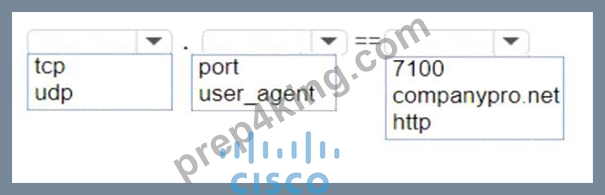
Answer:
Explanation: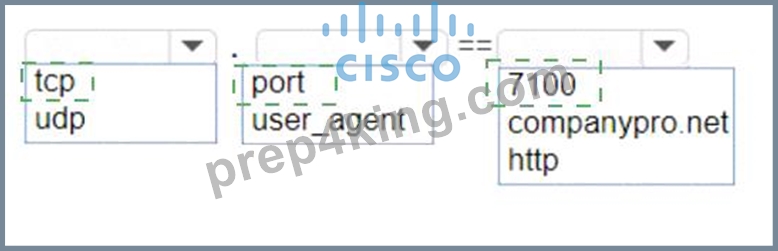
Explanation:
To capture packets sent to and received from the URLhttps://www.companypro.net:7100/apiusing Wireshark, you would use the following filter options:
* Protocol:tcp
* Filter Type:port
* Port Number:7100
This filter setup in Wireshark will display all TCP packets that are sent to or received from port 7100, which is the port specified in the URL for the API service. Since HTTPS typically uses TCP as the transport layer protocol, filtering by TCP and the specific port number will help isolate the relevant packets for troubleshooting the app's data download issues.
* cp: The app is using HTTPS, which relies on the TCP protocol for communication.
* port: The specific port number used by the application, which in this case is 7100.
* 7100: This is the port specified in the URL (https://www.companypro.net:7100/api).
This filter will capture all TCP traffic on port 7100, allowing you to analyze the packets related to the application's data download.
References:
* Wireshark Filters: Wireshark Display Filters
NEW QUESTION # 28
Which two pieces of information should you include when you initially create a support ticket? (Choose 2.)
- A. A description of the conditions when the fault occurs
- B. The description of the top-down fault-finding procedure
- C. Details about the computers connected to the network
- D. The actions taken to resolve the fault
- E. A detailed description of the fault
Answer: A,E
Explanation:
* Statement A: "A detailed description of the fault." This is essential for support staff to understand the nature of the problem and begin troubleshooting effectively.
* Statement C: "A description of the conditions when the fault occurs." This helps in reproducing the issue and identifying patterns that might indicate the cause of the fault.
* Statement B: "Details about the computers connected to the network." While useful, this is not as immediately critical as understanding the fault itself and the conditions under which it occurs.
* Statement D: "The actions taken to resolve the fault." This is important but typically follows the initial report.
* Statement E: "The description of the top-down fault-finding procedure." This is more of a troubleshooting methodology than information typically included in an initial support ticket.
References:
* Best Practices for Submitting Support Tickets: Support Ticket Guidelines
NEW QUESTION # 29
A local company requires two networks in two new buildings. The addresses used in these networksmust be in the private network range.
Which two address ranges should the company use? (Choose 2.)
Note: You will receive partial credit for each correct selection.
- A. 192.16.0.0 to 192.16.255.255
- B. 172.16.0.0 to 172.31.255.255
- C. 192.168.0.0 to 192.168.255.255
- D. 11.0.0.0 to 11.255.255.255
Answer: B,C
Explanation:
The private IP address ranges that are set aside specifically for use within private networks and not routable on the internet are as follows:
* Class A: 10.0.0.0 to 10.255.255.255
* Class B: 172.16.0.0 to 172.31.255.255
* Class C: 192.168.0.0 to 192.168.255.255
These ranges are defined by the Internet Assigned Numbers Authority (IANA) and are used for local communications within a private network123.
Given the options: A.172.16.0.0 to 172.31.255.255falls within the Class B private range. B.192.16.0.0 to
192.16.255.255is not a recognized private IP range. C.11.0.0.0 to 11.255.255.255is not a recognized private IP range. D.192.168.0.0 to 192.168.255.255falls within the Class C private range.
Therefore, the correct selections that the company should use for their private networks areAandD.
References:=
* Reserved IP addresses on Wikipedia
* Private IP Addresses in Networking - GeeksforGeeks
* Understanding Private IP Ranges, Uses, Benefits, and Warnings
NEW QUESTION # 30
During the data encapsulation process, which OSI layer adds a header that contains MAC addressing information and a trailer used for error checking?
- A. Session
- B. Transport
- C. Data Link
- D. Network
Answer: C
Explanation: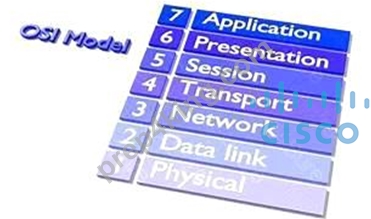
OSI model
During the data encapsulation process, theData Link layerof the OSI model is responsible for adding a header that contains MAC addressing information and a trailer used for error checking.The header typically includes the source and destination MAC addresses, while the trailer contains a Frame Check Sequence (FCS) which is used for error detection1.
The Data Link layer ensures that messages are delivered to the proper device on a LAN using hardware addresses and translates messages from the Network layer into bits for the Physical layer to transmit. It also controls how data is placed onto the medium and is received from the medium through the physical hardware.
References:=
* The OSI Model - The 7 Layers of Networking Explained in Plain English
* OSI Model - Network Direction
* Which layer adds both header and trailer to the data?
* What is OSI Model | 7 Layers Explained - GeeksforGeeks
NEW QUESTION # 31
A host is given the IP address 172.16.100.25 and the subnet mask 255.255.252.0.
What is the CIDR notation for this address?
- A. 172.16.100.25 /23
- B. 172.16.100.25 /21
- C. 172.16.100.25 /22
- D. 172.16.100.25 /20
Answer: C
Explanation:
The CIDR (Classless Inter-Domain Routing) notation for the subnet mask 255.255.252.0 is /22. This notation indicates that the first 22 bits of the IP address are used for network identification, and the remaining bits are used for host addresses within the network1.
References :=
*Subnet Cheat Sheet - 24 Subnet Mask, 30, 26, 27, 29, and other IP Address CIDR Network References
*Subnet Mask to CIDR Notation: The given subnet mask is 255.255.252.0. To convert this to CIDR notation:
*Convert the subnet mask to binary: 11111111.11111111.11111100.00000000
*Count the number of consecutive 1s in the binary form: There are 22 ones.
*Therefore, the CIDR notation is /22.
References:
*Understanding Subnetting and CIDR: Cisco CIDR Guide
NEW QUESTION # 32
A user reports that a company website is not available. The help desk technician issues a tracert command to determine if the server hosting the website isreachable over the network. The output of the command is shown as follows: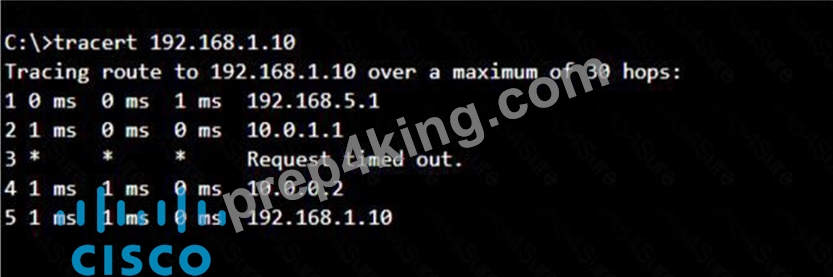
What can you tell from the command output?
- A. The server with the address 192.168.1.10 is reachable over the network.
- B. Requests to the web server at 192.168.1.10 are being delayed and time out.
- C. The router at hop 3 is not forwarding packets to the IP address 192.168.1.10.
- D. The server address 192.168.1.10 is being blocked by a firewall on the router at hop 3.
Answer: A
Explanation:
The tracert command output shows the path taken to reach the destination IP address, 192.168.1.10. The command output indicates:
*Hops 1 and 2 are successfully reached.
*Hop 3 times out, meaning the router at hop 3 did not respond to the tracert request. However, this does not necessarily indicate a problem with forwarding packets, as some routers may be configured to block or not respond to ICMP requests.
*Hops 4 and 5 are successfully reached, with hop 5 being the destination IP 192.168.1.10, indicating that the server is reachable.
Thus, the correct answer is C. The server with the address 192.168.1.10 is reachable over the network.
References :=
*Cisco Traceroute Command
*Understanding Traceroute
The tracert command output indicates that the server with the address 192.168.1.10 is reachable over the network. The asterisk (*) at hop 3 suggests that the probe sent to that hop did not return a response, which could be due to a variety of reasons such as a firewall blocking ICMP packets or the router at that hop being configured not to respond to ICMP requests. However, since the subsequent hops (4 and 5) are showing response times, it means that the packets are indeed getting through and the server is reachable12.
References :=
*How to Use Traceroute Command to Read Its Results
*How to Use the Tracert Command in Windows
NEW QUESTION # 33
A user initiates a trouble ticket stating that an external web page is not loading. You determine that other resources both internal and external are still reachable.
Which command can you use to help locate where the issue is in the network path to the external web page?
- A. ipconfig/all
- B. nslookup
- C. tracert
- D. ping -t
Answer: C
Explanation:
The tracert command is used to determine the route taken by packets across an IP network. When a user reports that an external web page is not loading, while other resources are accessible, it suggests there might be an issue at a certain point in the network path to the specific web page. The tracert command helps to diagnose where the breakdown occurs by displaying a list of routers that the packets pass through on their way to the destination. It can identify the network segment where the packets stop progressing, which is valuable for pinpointing where the connectivity issue lies. References := Cisco CCST Networking Certification FAQs - CISCONET Training Solutions, Command Prompt (CMD): 10 network-related commands you should know, Network Troubleshooting Commands Guide: Windows, Mac & Linux - Comparitech, How to Use the Traceroute and Ping Commands to Troubleshoot Network, Network Troubleshooting Techniques: Ping, Traceroute, PathPing.
*tracert Command: This command is used to determine the path packets take to reach a destination. It lists all the hops (routers) along the way and can help identify where the delay or failure occurs.
*ping -t: This command sends continuous ping requests and is useful for determining if a host is reachable but does not provide path information.
*ipconfig /all: This command displays all current TCP/IP network configuration values and can be used to verify network settings but not to trace a network path.
*nslookup: This command queries the DNS to obtain domain name or IP address mapping, useful for DNS issues but not for tracing network paths.
References:
*Microsoft tracert Command: tracert Command Guide
*Troubleshooting Network Issues with tracert: Network Troubleshooting Guide
NEW QUESTION # 34
What is the most compressed valid format of the IPv6 address 2001 :0db8:0000:0016:0000:001b: 2000:0056?
- A. 2001:db8: : 16: : 1b:2:56
- B. 2001:db8: : 16: : 1b: 2000: 56
- C. 2001:db8: 0:16: :1b: 2000:56
- D. 2001:db8: 16: :1b:2:56
Answer: C
Explanation:
IPv6 addresses can be compressed by removing leading zeros and replacing consecutive groups of zeros with a double colon (::). Here's how to compress the address 2001:0db8:0000:0016:0000:001b:2000:0056:
* Remove leading zeros from each segment:
* 2001:db8:0000:0016:0000:001b:2000:0056 becomes 2001:db8:0:16:0:1b:2000:56
* Replace the longest sequence of consecutive zeros with a double colon (::). In this case, the two consecutive zeros between the 16 and 1b:
* 2001:db8:0:16::1b:2000:56
Thus, the most compressed valid format of the IPv6 address is 2001:db8:0:16::1b:2000:56.
References:=
* Cisco Learning Network
* IPv6 Addressing (Cisco)
NEW QUESTION # 35
A support technician examines the front panel of a Cisco switch and sees 4 Ethernet cables connected in the first four ports. Ports 1, 2, and 3 have a green LED. Port 4 has a blinking green light.
What is the state of the Port 4?
- A. Link is up with cable malfunctions.
- B. Link is up and not stable.
- C. Link is up and there is no activity.
- D. Link is up and active.
Answer: D
Explanation:
On a Cisco switch, a port with a blinking green LED typically indicates that the port is up (active) and is currently transmitting or receiving data. This is a normal state indicating active traffic on the port.
*A. Link is up with cable malfunctions: Usually indicated by an amber or blinking amber light.
*B. Link is up and not stable: Not typically indicated by a green blinking light.
*D. Link is up and there is no activity: Would be indicated by a solid green light withoutblinking.
Thus, the correct answer is C. Link is up and active.
References :=
*Cisco Switch LED Indicators
*Cisco Ethernet Switch LED Patterns
NEW QUESTION # 36
A help desk technician receives the four trouble tickets listed below. Which ticket should receive the highest priority and be addressed first?
- A. Ticket 4: Two users report that wireless access in the cafeteria has been down for the last hour.
- B. Ticket 3: A user reports that response time for a cloud-based application is slower than usual.
- C. Ticket 1: A user requests relocation of a printer to a different network jack in the same office. The jack must be patched and made active.
- D. Ticket 2: An online webinar is taking place in the conference room. The video conferencing equipment lost internet access.
Answer: D
NEW QUESTION # 37
Computers in a small office are unable to access companypro.net. You run the ipconfig command on one of the computers. The results are shown in the exhibit.
You need to determine if you can reach the router.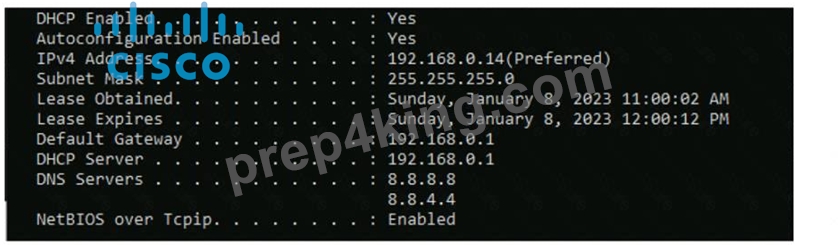
Which command should you use? Complete the command by selecting the correct options from each drop-down lists.
Answer:
Explanation: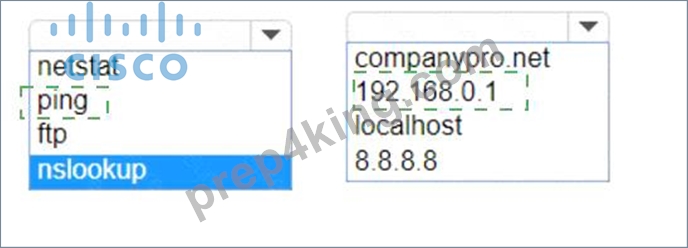
Explanation:
To determine if you can reach the router, you should use thepingcommand followed by the IP address of the router. Thepingcommand is a network utility used to test the reachability of a host on an Internet Protocol (IP) network and to measure the round-trip time for messages sent from the originating host to a destination computer.
The Default Gateway in theipconfigresults is typically the router's IP address in a home or small office network. In this case, the Default Gateway is192.168.0.1, which is the address you would ping to check connectivity to the router.
References:=
* How to Use the Ping Command
* Testing Network Connectivity with the Ping Command
To determine if you can reach the router, you should use thepingcommand with the IP address of the router.
* Command:ping
* Target:192.168.0.1
So, the completed command is:
* ping 192.168.0.1
Step by Step Comprehensive and Detailed Explanation:
* ping: The ping command sends ICMP Echo Request messages to the target IP address and waits for an Echo Reply. It is commonly used to test the reachability of a network device.
* 192.168.0.1: This is the IP address of the default gateway (the router) as shown in theipconfigoutput.
Pinging this address will help determine if the computer can communicate with the router.
References:
* Using the ping Command: ping Command Guide
NEW QUESTION # 38
......
Provide Valid Dumps To Help You Prepare For Cisco Certified Support Technician (CCST) NetworkingExam Exam: https://www.prep4king.com/CCST-Networking-exam-prep-material.html
CCST-Networking Dumps Questions [2024] Pass for Exam: https://drive.google.com/open?id=1e1QvuM_pPrH3lVahGCCt3CWjThG19SEy
