

Check Real Cisco 300-730 Exam Question for Free (2023)
Get Ready to Boost your Prepare for your 300-730 Exam with 100 Questions
NEW QUESTION 14
Which two remote access VPN solutions support SSL? (Choose two.)
- A. clientless
- B. FlexVPN
- C. Cisco AnyConnect
- D. L2TP
- E. EZVPN
Answer: A,C
NEW QUESTION 15 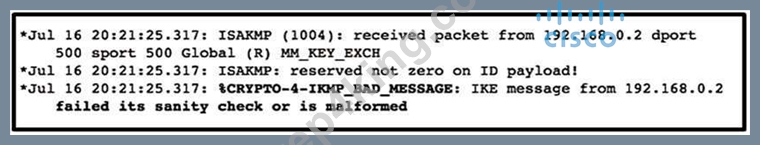
Refer to the exhibit. Which type of mismatch is causing the problem with the IPsec VPN tunnel?
- A. crypto access list
- B. Phase 1 policy
- C. preshared key
- D. transform set
Answer: C
Explanation:
Section: Troubleshooting using ASDM and CLI
Explanation/Reference: https://www.cisco.com/c/en/us/support/docs/security-vpn/ipsec-negotiation-ike-protocols/5409- ipsec-debug-00.html#ike
NEW QUESTION 16
Which VPN solution uses TBAR?
- A. DMVPN
- B. VTI
- C. Cisco AnyConnect
- D. GETVPN
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_getvpn/configuration/xe-3s/sec-get- vpn-xe-3s-book/sec-get-vpn.html
NEW QUESTION 17
Which two changes must be made in order to migrate from DMVPN Phase 2 to Phase 3 when EIGRP is configured? (Choose two.)
- A. Add NHRP redirects on the hub.
- B. Add NHRP shortcuts on the hub.
- C. Disable EIGRP next-hop-self on the hub.
- D. Enable EIGRP next-hop-self on the hub.
- E. Add NHRP redirects on the spoke.
Answer: A,C
NEW QUESTION 18
Refer to the exhibit.
Which value must be configured in the User Group field when the Cisco AnyConnect Profile is created to connect to an ASA headend with IPsec as the primary protocol?
- A. group-policy
- B. tunnel-group
- C. group-alias
- D. address-pool
Answer: B
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/vpn_client/anyconnect/anyconnect41/ administration/guide/b_AnyConnect_Administrator_Guide_4-1/configure-vpn.html
NEW QUESTION 19
A Cisco ASA is configured in active/standby mode. What is needed to ensure that Cisco AnyConnect users can connect after a failover event?
- A. Configure a backup server in the XML profile.
- B. The vpnsession-db must be cleared manually.
- C. AnyConnect images must be uploaded to both failover ASA devices.
- D. AnyConnect client must point to the standby IP address.
Answer: C
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa90/configuration/guide/asa_90_cli_config/ ha_active_standby.html
NEW QUESTION 20
Which feature allows the ASA to handle nonstandard applications and web resources so that they display correctly over a clientless SSL VPN connection?
- A. plug-ins
- B. WebType ACL
- C. Smart Tunnel
- D. single sign-on
Answer: C
NEW QUESTION 21
What is a requirement for smart tunnels to function properly?
- A. Stateful failover must not be configured.
- B. The user on the client machine must have admin access.
- C. Applications must be UDP.
- D. Java or ActiveX must be enabled on the client machine.
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/support/docs/security/asa-5500-x-series-next-generation- firewalls/111007-smart-tunnel-asa-00.html
NEW QUESTION 22
Refer to the exhibit.
The IKEv2 site-to-site VPN tunnel between two routers is down. Based on the debug output, which type of mismatch is the problem?
- A. ikev2 proposal
- B. peer identity
- C. transform set
- D. preshared key
Answer: B
NEW QUESTION 23 
Refer to the exhibit. Based on the debug output, which type of mismatch is preventing the VPN from coming up?
- A. interesting traffic
- B. PFS
- C. lifetime
- D. preshared key
Answer: C
Explanation:
Section: Troubleshooting using ASDM and CLI
Explanation:
If the responder's policy does not allow it to accept any part of the proposed Traffic Selectors, it responds with a TS_UNACCEPTABLE Notify message.
NEW QUESTION 24
Cisco AnyConnect Secure Mobility Client has been configured to use IKEv2 for one group of users and SSL for another group. When the administrator configures a new AnyConnect release on the Cisco ASA, the IKEv2 users cannot download it automatically when they connect. What might be the problem?
- A. The new client image does not use the same major release as the current one.
- B. Client software updates are not supported with IKEv2.
- C. Client services are not enabled.
- D. The XML profile is not configured correctly for the affected users.
Answer: C
NEW QUESTION 25
Which method dynamically installs the network routes for remote tunnel endpoints?
- A. policy-based routing
- B. route filtering
- C. reverse route injection
- D. CEF
Answer: C
Explanation:
Section: Site-to-site Virtual Private Networks on Routers and Firewalls Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_vpnav/configuration/12-4t/sec-vpn- availability-12-4t-book/sec-rev-rte-inject.html
NEW QUESTION 26
Which technology works with IPsec stateful failover?
- A. GRE
- B. GLBR
- C. VRRP
- D. HSRP
Answer: D
Explanation:
Section: Secure Communications Architectures
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/ios/12_2/12_2y/12_2yx11/feature/guide/ ft_vpnha.html#wp1122512
NEW QUESTION 27
In a FlexVPN deployment, the spokes successfully connect to the hub, but spoke-to-spoke tunnels do not form. Which troubleshooting step solves the issue?
- A. Verify that the tunnel interface is contained within a VRF.
- B. Verify the hub configuration to check if the NHRP shortcut is enabled.
- C. Verify the spoke configuration to check if the NHRP redirect is enabled.
- D. Verify that the spoke receives redirect messages and sends resolution requests.
Answer: D
NEW QUESTION 28
A network engineer must design a clientless VPN solution for a company. VPN users must be able to access several internal web servers. When reachability to those web servers was tested, it was found that one website is not being rewritten correctly by the ASA.
What is a potential solution for this issue while still allowing it to be a clientless VPN setup?
- A. Set up a smart tunnel with the IP address of the web server.
- B. Set up Cisco AnyConnect with a split tunnel that has the IP address of the web server.
- C. Set up a NAT rule that translates the ASA public address to the web server private address on port 80.
- D. Set up a WebACL to permit the IP address of the web server.
Answer: A
NEW QUESTION 29
Which technology works with IPsec stateful failover?
- A. GRE
- B. GLBR
- C. VRRP
- D. HSRP
Answer: D
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/ios/12_2/12_2y/12_2yx11/feature/guide/ ft_vpnha.html#wp1122512
NEW QUESTION 30
Refer to the exhibit.
Which type of VPN implementation is displayed?
- A. IKEv2 load balancer
- B. IKEv1 cluster
- C. IKEv2 reconnect
- D. IKEv2 backup gateway
Answer: A
NEW QUESTION 31
Which two commands help determine why the NHRP registration process is not being completed even after the IPsec tunnel is up? (Choose two.)
- A. show crypto ipsec sa
- B. show dmvpn detail
- C. show ip nhrp traffic
- D. show ip traffic
- E. show crypto isakmp sa
Answer: C,E
Explanation:
Section: Secure Communications Architectures
NEW QUESTION 32
A second set of traffic selectors is negotiated between two peers using IKEv2. Which IKEv2 packet will contain details of the exchange?
- A. IKEv2 IKE_SA_INIT
- B. IKEv2 INFORMATIONAL
- C. IKEv2 IKE_AUTH
- D. IKEv2 CREATE_CHILD_SA
Answer: B
Explanation:
Section: Site-to-site Virtual Private Networks on Routers and Firewalls Explanation/Reference:
NEW QUESTION 33
Which method dynamically installs the network routes for remote tunnel endpoints?
- A. policy-based routing
- B. route filtering
- C. reverse route injection
- D. CEF
Answer: C
Explanation:
Reference:
<https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_conn_vpnav/configuration/12-4t/sec-vpn- availability-12-4t-book/sec-rev-rte-inject.html>
NEW QUESTION 34
Refer to the exhibit.
All internal clients behind the ASA are port address translated to the public outside interface that has an IP address of 3.3.3.3. Client 1 and client 2 have established successful SSL VPN connections to the ASA. What must be implemented so that "3.3.3.3" is returned from a browser search on the IP address?
- A. Tunnel All Networks under Group Policy
- B. Same-security-traffic permit inter-interface under Group Policy
- C. Exclude Network List Below under Group Policy
- D. Tunnel Network List Below under Group Policy
Answer: D
NEW QUESTION 35
What uses an Elliptic Curve key exchange algorithm?
- A. SHA
- B. ECDSA
- C. AES-GCM
- D. ECDHE
Answer: D
Explanation:
Reference:
https://blog.cloudflare.com/a-relatively-easy-to-understand-primer-on-elliptic-curve-cryptography/
NEW QUESTION 36
......
Use Free 300-730 Exam Questions that Stimulates Actual EXAM : https://www.prep4king.com/300-730-exam-prep-material.html
Get 100% Real 300-730 Free Online Practice Test: https://drive.google.com/open?id=1Dfw5huyBw4XbNamo91grVbHX7ipOuc7x
