

FCSS_SASE_AD-24 Dumps To Pass Fortinet Exam in 24 Hours - Prep4King
Buy Latest FCSS_SASE_AD-24 Exam Q&A PDF - One Year Free Update
NEW QUESTION # 20
When viewing the daily summary report generated by FortiSASE. the administrator notices that the report contains very little data. What is a possible explanation for this almost empty report?
- A. There are no security profile group applied to all policies.
- B. The web filter security profile is not set to Monitor
- C. Log allowed traffic is set to Security Events for all policies.
- D. Digital experience monitoring is not configured.
Answer: C
Explanation:
If "Log allowed traffic" is set only to "Security Events" for all policies, only specific security events (such as blocked or malicious traffic) are logged, while general allowed traffic is not recorded.
This results in a daily summary report with minimal data, as it lacks logs of most regular traffic. To capture more detailed information, "Log allowed traffic" should be configured to record all traffic types, not just security events.
NEW QUESTION # 21
Which endpoint functionality can you configure using FortiSASE?
Response:
- A. You can enable and push web filter to FortiClient endpoints.
- B. You can configure inline sandbox to scan zero-day malware attacks.
- C. Site-based FortiExtender users can perform on-demand vulnerability scans.
- D. It can be applied to both SWG and VPN deployments.
Answer: B
NEW QUESTION # 22
Which two additional components does FortiSASE use for application control to act as an inline-CASB?
(Choose two.)
- A. SSL deep inspection
- B. DNS filter
- C. Web filter with inline-CASB
- D. intrusion prevention system (IPS)
Answer: A,D
NEW QUESTION # 23
Which FortiSASE feature can you use to see a list of Software-as-a-Service (SaaS) applications and health-check metrics for first-mile connectivity between the geographical points of presence (PoPs) provisioned for your FortiSASE instance and these SaaS applications?
- A. digital experience monitoring DEM
- B. FortiView
- C. security logs
- D. event logs
Answer: A
NEW QUESTION # 24
Refer to the exhibit.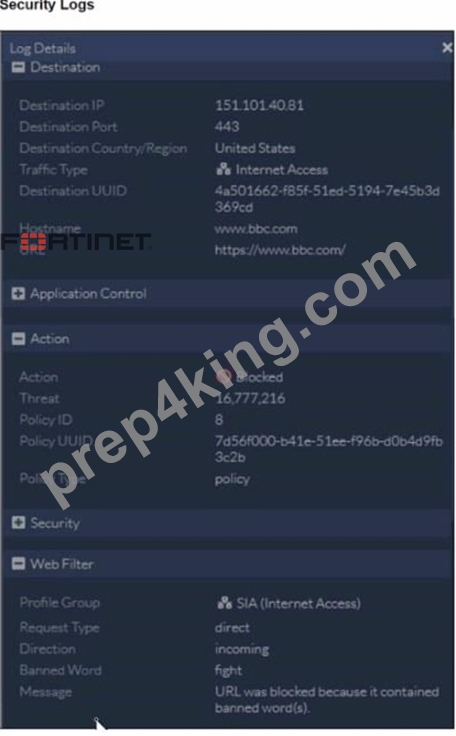
To allow access, which web tiller configuration must you change on FortiSASE?
- A. FortiGuard category-based filter
- B. inline cloud access security broker (CASB) headers
- C. URL Filter
- D. content filter
Answer: D
NEW QUESTION # 25
Which FortiSASE components are critical for protecting remote users?
(Select all that apply)
Response:
- A. Zero Trust Network Access (ZTNA)
- B. Secure Web Gateway (SWG)
- C. Data Loss Prevention (DLP)
- D. Secure SD-WAN
Answer: A,B,C
NEW QUESTION # 26
Which three configurations must you perform to set up FortiGate as a FortiSASE LAN extension? (Choose three.)
- A. Create a LAN extension VDOM on the edge FortiGate
- B. Configure VXLAN-over-IPsecon the FortiSASE portal
- C. Authorize the edge FortiGate device on FortiSASE portal.
- D. Enter the FortiSASE domain name in the FortiGate GUI as the access controller address.
- E. Connect FortiGate to FortiSASE using FortiZTP.
Answer: A,C,D
NEW QUESTION # 27
A customer needs to implement device posture checks for their remote endpoints while accessing the protected server. They also want the TCP traffic between the remote endpoints and the protected servers to be processed by FortiGate.
In this scenario, which three setups will achieve the above requirements? (Choose three.)
- A. Configure private access policies on FortiSASE with ZTNA.
- B. Configure ZTNA servers and ZTNA policies on FortiGate.
- C. Sync ZTNA tags from FortiSASE to FortiGate.
- D. Configure ZTNA tags on FortiGate.
- E. Configure FortiGate as a zero trust network access (ZTNA) access proxy.
Answer: B,D,E
Explanation:
To meet the requirements of implementing device posture checks for remote endpoints and ensuring that TCP traffic between the endpoints and protected servers is processed by FortiGate, the following three setups are necessary:
Configure ZTNA tags on FortiGate (Option A):
ZTNA (Zero Trust Network Access) tags are used to define access control policies based on the security posture of devices. By configuring ZTNA tags on FortiGate, administrators can enforce granular access controls, ensuring that only compliant devices can access protected resources.
Configure FortiGate as a zero trust network access (ZTNA) access proxy (Option B):
FortiGate can act as a ZTNA access proxy, which allows it to mediate and secure connections between remote endpoints and protected servers. This setup ensures that all TCP traffic passes through FortiGate, enabling inspection and enforcement of security policies.
Configure ZTNA servers and ZTNA policies on FortiGate (Option C):
To enable ZTNA functionality, administrators must define ZTNA servers (the protected resources) and create ZTNA policies on FortiGate. These policies determine how traffic is routed, inspected, and controlled based on device posture and user identity.
NEW QUESTION # 28
When accessing the FortiSASE portal for the first time, an administrator must select data center locations for which three FortiSASE components? (Choose three.)
- A. Logging
- B. Authentication
- C. SD-WAN hub
- D. Endpoint management
- E. Points of presence
Answer: A,D,E
Explanation:
When accessing the FortiSASE portal for the first time, an administrator must select data center locations for the following FortiSASE components:
Endpoint Management:
The data center location for endpoint management ensures that endpoint data and policies are managed and stored within the chosen geographical region.
Points of Presence (PoPs):
Points of Presence (PoPs) are the locations where FortiSASE services are delivered to users.
Selecting PoP locations ensures optimal performance and connectivity for users based on their geographical distribution.
Logging:
The data center location for logging determines where log data is stored and managed. This is crucial for compliance and regulatory requirements, as well as for efficient log analysis and reporting.
NEW QUESTION # 29
Which FortiOS command is used to view the log settings configured in FortiSASE?
Response:
- A. diagnose debug log
- B. get system log settings
- C. config log settings view
- D. get log settings
Answer: B
NEW QUESTION # 30
Which onboarding method is most effective for securely integrating a large number of remote users into FortiSASE?
Response:
- A. Temporary guest accounts with limited access
- B. Bulk user registration through automated scripts
- C. Individual user registration via email invitations
- D. Open registration allowing user self-enrollment
Answer: B
NEW QUESTION # 31
When you configure FortiSASE Secure Private Access (SPA) with SD-WAN integration, you must establish a routing adjacency between FortiSASE and the FortiGate SD-WAN hub. Which routing protocol must you use?
- A. OSPF
- B. IS-IS
- C. EIGRP
- D. BGP
Answer: D
Explanation:
When configuring FortiSASE Secure Private Access (SPA) with SD-WAN integration, establishing a routing adjacency between FortiSASE and the FortiGate SD-WAN hub requires the use of the Border Gateway Protocol (BGP).
* BGP (Border Gateway Protocol):
* BGP is widely used for establishing routing adjacencies between different networks, particularly in SD-WAN environments.
* It provides scalability and flexibility in managing dynamic routing between FortiSASE and the FortiGate SD-WAN hub.
* Routing Adjacency:
* BGP enables the exchange of routing information between FortiSASE and the FortiGate SD- WAN hub.
* This ensures optimal routing paths and efficient traffic management across the hybrid network.
References:
FortiOS 7.2 Administration Guide: Provides information on configuring BGP for SD-WAN integration.
FortiSASE 23.2 Documentation: Details on setting up routing adjacencies using BGP for Secure Private Access with SD-WAN.
NEW QUESTION # 32
You are designing a new network for Company X and one of the new cybersecurity policy requirements is that all remote user endpoints must always be connected and protected Which FortiSASE component facilitates this always-on security measure?
- A. unified FortiClient
- B. site-based deployment
- C. inline-CASB
- D. thin-branch SASE extension
Answer: A
Explanation:
The unified FortiClient component of FortiSASE facilitates the always-on security measure required for ensuring that all remote user endpoints are always connected and protected.
* Unified FortiClient:
* FortiClient is a comprehensive endpoint security solution that integrates with FortiSASE to provide continuous protection for remote user endpoints.
* It ensures that endpoints are always connected to the FortiSASE infrastructure, even when users are off the corporate network.
* Always-On Security:
* The unified FortiClient maintains a persistent connection to FortiSASE, enforcing security policies and protecting endpoints against threats at all times.
* This ensures compliance with the cybersecurity policy requiring constant connectivity and protection for remote users.
References:
FortiOS 7.2 Administration Guide: Provides information on configuring and managing FortiClient for endpoint security.
FortiSASE 23.2 Documentation: Explains how FortiClient integrates with FortiSASE to deliver always-on security for remote endpoints.
NEW QUESTION # 33
Which statement best describes the Digital Experience Monitor (DEM) feature on FortiSASE?
- A. It provides end-to-end network visibility from all the FortiSASE security PoPs to a specific SaaS application.
- B. It can be used to request a detailed analysis of the endpoint from the FortiGuard team.
- C. It requires a separate DEM agent to be downloaded from the FortiSASE portal and installed on the endpoint.
- D. It can help IT and security teams ensure consistent security monitoring for remote users.
Answer: A
Explanation:
The Digital Experience Monitor (DEM) feature in FortiSASE is designed to provide end-to-end network visibility by monitoring the performance and health of connections between FortiSASE security Points of Presence (PoPs) and specific SaaS applications. This ensures that administrators can identify and troubleshoot issues related to latency, jitter, packet loss, and other network performance metrics that could impact user experience when accessing cloud-based services.
Here's why the other options are incorrect:
B . It can be used to request a detailed analysis of the endpoint from the FortiGuard team: This is incorrect because DEM focuses on network performance monitoring, not endpoint analysis. Endpoint analysis would typically involve tools like FortiClient or FortiEDR, not DEM.
C . It requires a separate DEM agent to be downloaded from the FortiSASE portal and installed on the endpoint: This is incorrect because DEM operates at the network level and does not require an additional agent to be installed on endpoints.
D . It can help IT and security teams ensure consistent security monitoring for remote users: While DEM indirectly supports security by ensuring optimal network performance, its primary purpose is to monitor and improve the digital experience rather than enforce security policies.
Reference:
Fortinet FCSS FortiSASE Documentation - Digital Experience Monitoring Overview FortiSASE Administration Guide - Configuring DEM
NEW QUESTION # 34
Refer to the exhibits.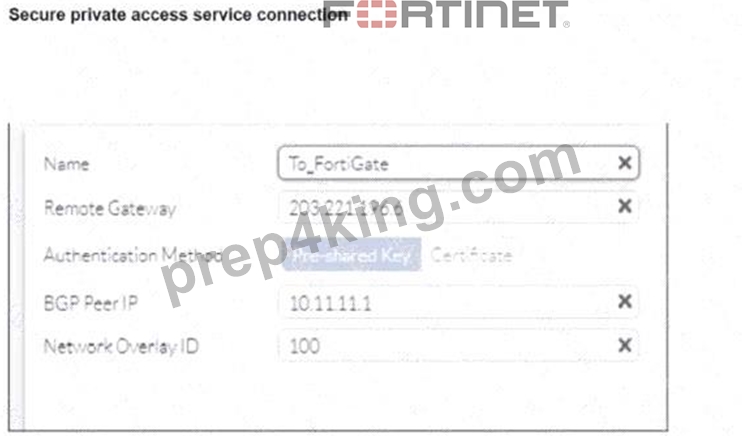
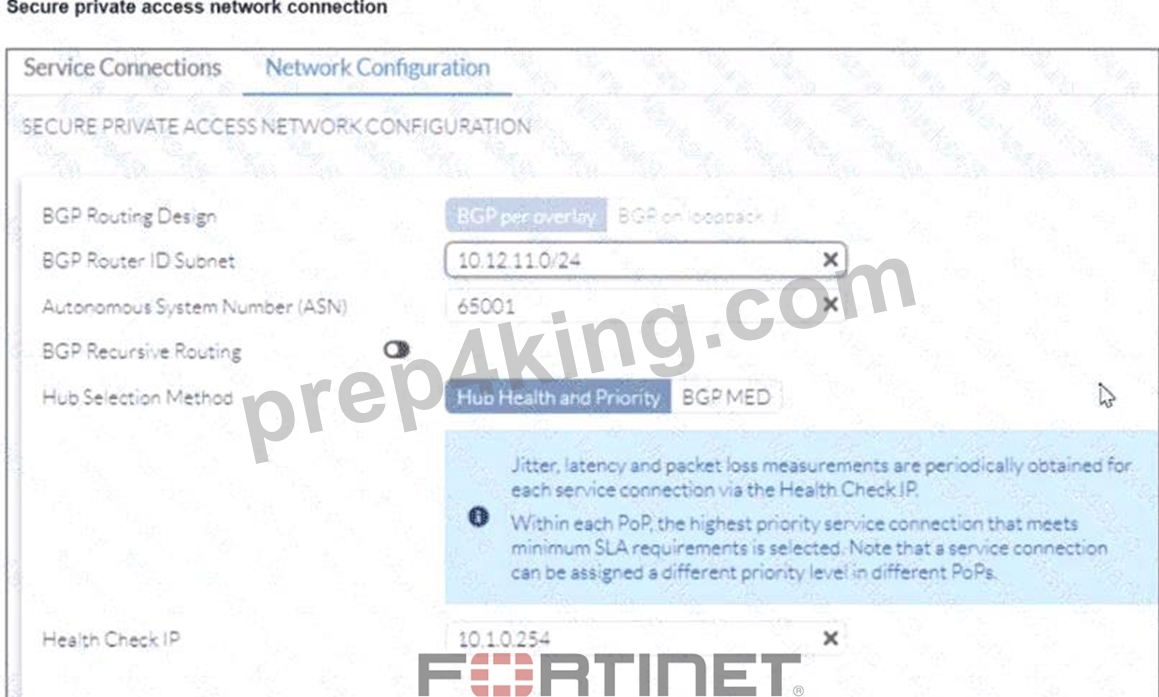
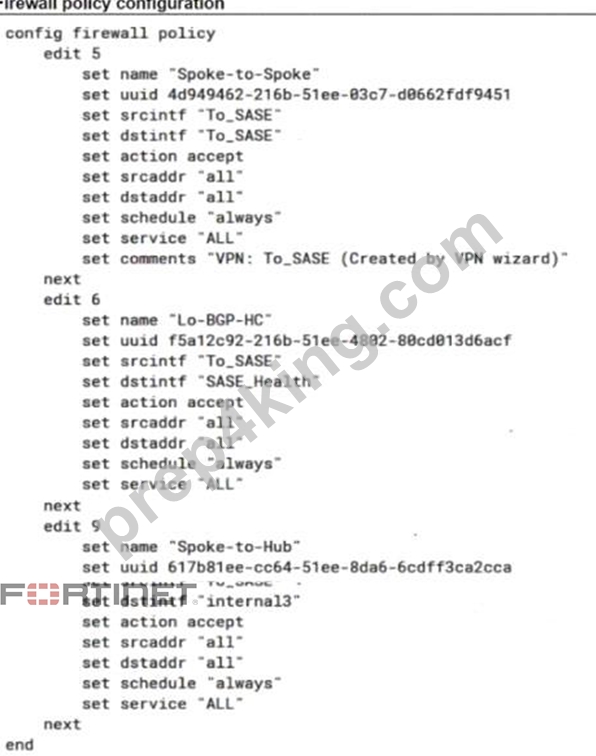
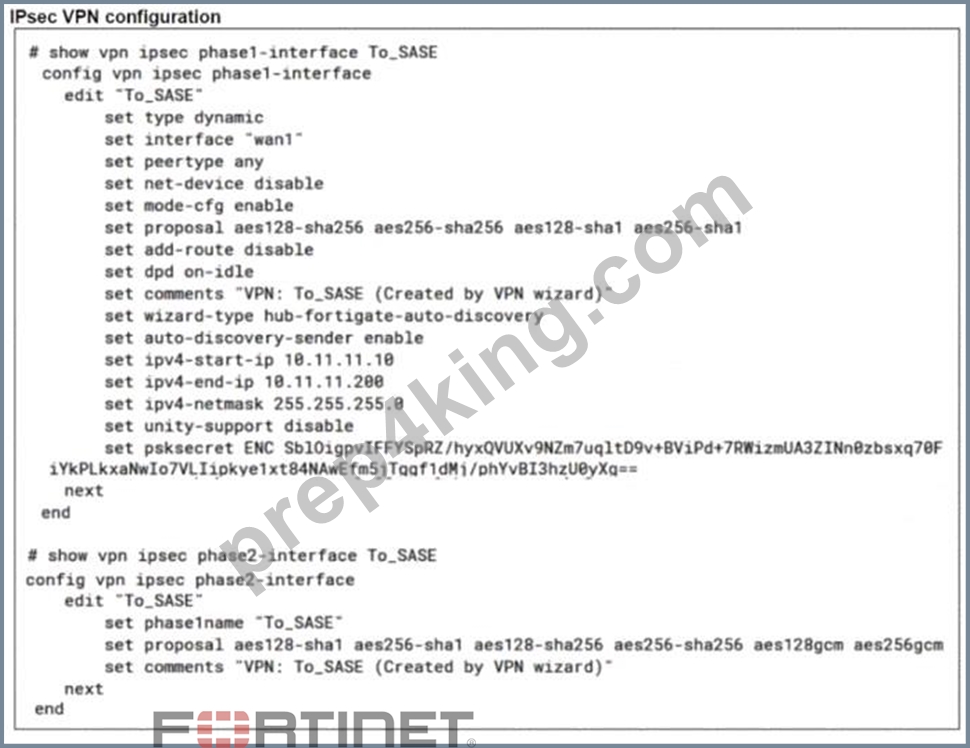
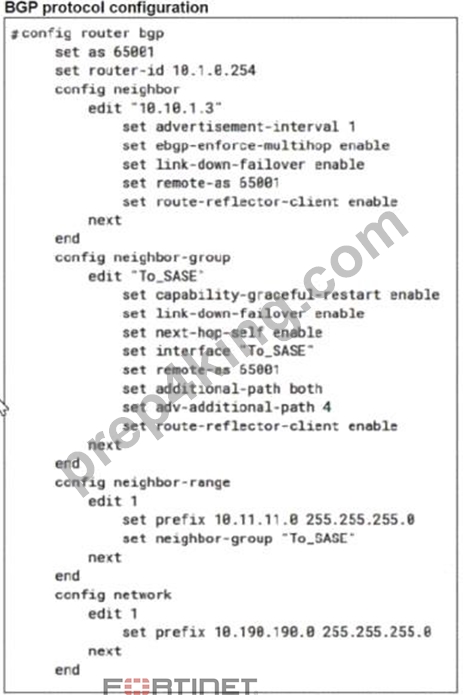
A FortiSASE administrator is trying to configure FortiSASE as a spoke to a FortiGate hub. The VPN tunnel does not establish Based on the provided configuration, what configuration needs to be modified to bring the tunnel up?
- A. NAT needs to be enabled in the Spoke-to-Hub firewall policy.
- B. FortiSASE spoke devices do not support mode config.
- C. The hub needs IKEv2 enabled in the IPsec phase 1 settings.
- D. The BGP router ID needs to match on the hub and FortiSASE.
Answer: C
NEW QUESTION # 35
Which element is essential for configuring security profiles in FortiSASE for content inspection?
Response:
- A. Data type
- B. Encryption type
- C. Application type
- D. User group
Answer: A
NEW QUESTION # 36
Zero Trust Network Access (ZTNA) within FortiSASE restricts access to applications based on user identity and device posture.
Response:
- A. True
- B. False
Answer: A
NEW QUESTION # 37
......
Fortinet FCSS_SASE_AD-24 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Download the Latest FCSS_SASE_AD-24 Dump - 2026 FCSS_SASE_AD-24 Exam Question Bank: https://www.prep4king.com/FCSS_SASE_AD-24-exam-prep-material.html
Latest Fortinet FCSS_SASE_AD-24 Certification Practice Test Questions: https://drive.google.com/open?id=1jH12HtrLGcRzWsK6QUtqvOPcMSnh_p2q
