
Prep and try our CKS valid and latest training questions & answers

Pass your test with the help of Linux Foundation CKS practice pdf. Prep4King offer 100% guarantee!
Updated: Oct 15, 2026
No. of Questions: 66 Questions & Answers with Testing Engine
Download Limit: Unlimited
Get free valid CKS study material and pass your exam test with confidence
We provide the most prestigious and reliable Prep4King CKS exam pdf for you. The valid questions with verified answers of CKS exam torrent will help you pass successfully. Download the Linux Foundation CKS free update questions and start your preparation right now.
100% Money Back Guarantee
Prep4King has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- 10 years of excellence
- 365 Days Free Updates
- Learn anywhere, anytime
- 100% Safe shopping experience
- Instant Download: Our system will send you the products you purchase in mailbox in a minute after payment. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
CKS Online Engine

- Online Tool, Convenient, easy to study.
- Instant Online Access
- Supports All Web Browsers
- Practice Online Anytime
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
- Try Online Engine Demo
CKS Self Test Engine

- Installable Software Application
- Simulates Real Exam Environment
- Builds CKS Exam Confidence
- Supports MS Operating System
- Two Modes For Practice
- Practice Offline Anytime
- Software Screenshots
CKS Practice Q&A's

- Printable CKS PDF Format
- Prepared by CKS Experts
- Instant Access to Download
- Study Anywhere, Anytime
- 365 Days Free Updates
- Free CKS PDF Demo Available
- Download Q&A's Demo
Linux Foundation CKS (Certified Kubernetes Security Specialist) Certification Exam is an industry-recognized certification that validates the skills and knowledge required to secure containerized applications and Kubernetes platforms. As more organizations adopt Kubernetes for their container orchestration, the demand for certified Kubernetes security specialists has increased. The CKS certification helps IT professionals demonstrate their expertise in securing Kubernetes environments and provides a competitive edge in the job market.
Reference: https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/#exams
Linux Foundation CKS (Certified Kubernetes Security Specialist) Certification Exam is an industry-recognized certification that validates a candidate's skills and knowledge in securing containerized applications and Kubernetes platforms. CKS exam is designed to test a candidate's ability to identify and address security risks in Kubernetes environments, as well as their proficiency in implementing security controls and best practices.
Linux Foundation CKS (Certified Kubernetes Security Specialist) exam is a certification program aimed at validating the skills of individuals in securing Kubernetes clusters. Kubernetes is a popular container orchestration platform used in cloud-native applications, and its security is paramount. CKS exam is designed to test the candidate's knowledge of various security concepts, tools, and practices that are essential in securing Kubernetes clusters.
Linux Foundation CKS Exam Overview:
| Certification Vendor: | The Linux Foundation |
|---|---|
| Exam Name: | Certified Kubernetes Security Specialist |
| Exam Number: | CKS |
| Certificate Validity Period: | 2 years |
| Available Languages: | English |
| Related Certifications: | CKA (Certified Kubernetes Administrator) |
| Exam Duration: | 120 minutes |
| Exam Price: | $395 USD |
| Exam Format: | Performance-based hands-on command line tasks |
| Passing Score: | 66% |
| Real Exam Qty: | 15-20 |
| Sample Questions: | Linux Foundation CKS Sample Questions |
| Exam Way: | Online proctored exam (remote) or at a testing center |
| Pre Condition: | CKA (Certified Kubernetes Administrator) certification is required before taking CKS |
| Official Syllabus URL: | https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/ |
Achieving the CKS certification demonstrates that an IT professional has mastered advanced Kubernetes security concepts and can effectively secure Kubernetes clusters in production environments. Certified Kubernetes Security Specialist (CKS) certification is recognized by the Cloud Native Computing Foundation (CNCF), which governs the Kubernetes project. As Kubernetes continues to be adopted by organizations, the need for Kubernetes security specialists will likely increase, making the CKS certification a valuable asset for IT professionals looking to advance their careers in this field.
Linux Foundation CKS Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Cluster Setup | 10% | - Understand the security implications of embedding cloud provider flags - Implement Pod-to-Pod encryption using mTLS or WireGuard - Use role-based access control (RBAC) to minimize exposure - Manage sensitive information in clusters - Use Cis benchmarks to check Kubernetes cluster settings - Configure TLS certificates and minimum version for etcd - Use Pod Security Policies to control security-related pod behaviors |
| Topic 2: Supply Chain Security | 20% | - Sign container images and verify signatures - Use image admission controllers to prevent use of untrusted images - Understand image security scanning and its workflow - Understand the software supply chain best practices - Minimize base image footprint - Use distroless images for static workload - Understand the container build process - Use static analysis tools to detect vulnerabilities |
| Topic 3: Minimize Microservice Vulnerabilities | 20% | - Use AppArmor or seccomp profiles to constrain container behavior - Use PSP to enforce security controls - Set appropriate security contexts for pods and containers - Use OPA Gatekeeper to enforce security controls - Understand the principle of immutable containers - Configure network policies for namespace isolation |
| Topic 4: Monitoring, Logging, and Runtime Security | 20% | - Falco - container security monitoring and threat detection - Understand and monitor network traffic - Perform behavioral analytics to detect malicious activity - Detect threats at the container level - Audit and detect logs and events for anomalies - Minimize the attack surface using container health indicators |
| Topic 5: System Hardening | 15% | - Understand the concept of OPA (Open Policy Agent) and Gatekeeper - Modify host components to improve security - Kernel defaults and parameters using sysctl - Enable audit logging |
| Topic 6: Cluster Hardening | 15% | - Minimize admission of containers with allowPrivilegeEscalation - Minimize admission of containers with sharing the host IPC namespace - Minimize admission of privileged containers - Minimize admission of containers with hostPath volumes - Minimize admission of containers without AppArmor profile - Minimize admission of containers without seccomp profiles - Minimize admission of containers without a security context - Minimize admission of containers that allow host namespaces - Minimize admission of containers with FlexVolume volumes - Minimize admission of containers with added capabilities - Minimize admission of containers with sharing the host network namespace - Minimize admission of containers with capabilities assigned - Minimize admission of containers with raw block devices - Minimize admission of containers with sharing the host process namespace |
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions:
SIMULATION
Enable audit logs in the cluster, To Do so, enable the log backend, and ensure that
1. logs are stored at /var/log/kubernetes/kubernetes-logs.txt.
2. Log files are retained for 5 days.
3. at maximum, a number of 10 old audit logs files are retained.
Edit and extend the basic policy to log:
1. Cronjobs changes at RequestResponse
2. Log the request body of deployments changes in the namespace kube-system.
3. Log all other resources in core and extensions at the Request level.
4. Don't log watch requests by the "system:kube-proxy" on endpoints or
Correct Answer:
See the Explanation belowExplanation:


SIMULATION
Task
Analyze and edit the given Dockerfile /home/candidate/KSSC00301/Docker file (based on the ubuntu:16.04 image), fixing two instructions present in the file that are prominent security/best-practice issues.
Analyze and edit the given manifest file /home/candidate/KSSC00301/deployment.yaml, fixing two fields present in the file that are prominent security/best-practice issues.

Correct Answer:
See the Explanation below
Explanation: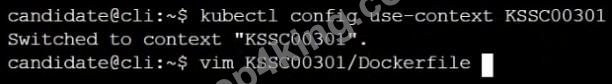


SIMULATION
Fix all issues via configuration and restart the affected components to ensure the new setting takes effect.
Fix all of the following violations that were found against the API server:- a. Ensure that the RotateKubeletServerCertificate argument is set to true.
b. Ensure that the admission control plugin PodSecurityPolicy is set.
c. Ensure that the --kubelet-certificate-authority argument is set as appropriate.
Fix all of the following violations that were found against the Kubelet:- a. Ensure the --anonymous-auth argument is set to false.
b. Ensure that the --authorization-mode argument is set to Webhook.
Fix all of the following violations that were found against the ETCD:-
a. Ensure that the --auto-tls argument is not set to true
b. Ensure that the --peer-auto-tls argument is not set to true
Hint: Take the use of Tool Kube-Bench
Correct Answer:
See the Explanation belowExplanation:
Fix all of the following violations that were found against the API server:- a. Ensure that the RotateKubeletServerCertificate argument is set to true.
apiVersion: v1
kind: Pod
metadata:
creationTimestamp: null
labels:
component: kubelet
tier: control-plane
name: kubelet
namespace: kube-system
spec:
containers:
- command:
- kube-controller-manager
+ - --feature-gates=RotateKubeletServerCertificate=true
image: gcr.io/google_containers/kubelet-amd64:v1.6.0
livenessProbe:
failureThreshold: 8
httpGet:
host: 127.0.0.1
path: /healthz
port: 6443
scheme: HTTPS
initialDelaySeconds: 15
timeoutSeconds: 15
name: kubelet
resources:
requests:
cpu: 250m
volumeMounts:
- mountPath: /etc/kubernetes/
name: k8s
readOnly: true
- mountPath: /etc/ssl/certs
name: certs
- mountPath: /etc/pki
name: pki
hostNetwork: true
volumes:
- hostPath:
path: /etc/kubernetes
name: k8s
- hostPath:
path: /etc/ssl/certs
name: certs
- hostPath:
path: /etc/pki
name: pki
b. Ensure that the admission control plugin PodSecurityPolicy is set.
audit: "/bin/ps -ef | grep $apiserverbin | grep -v grep"
tests:
test_items:
- flag: "--enable-admission-plugins"
compare:
op: has
value: "PodSecurityPolicy"
set: true
remediation: |
Follow the documentation and create Pod Security Policy objects as per your environment.
Then, edit the API server pod specification file $apiserverconf
on the master node and set the --enable-admission-plugins parameter to a value that includes PodSecurityPolicy :
--enable-admission-plugins=...,PodSecurityPolicy,...
Then restart the API Server.
scored: true
c. Ensure that the --kubelet-certificate-authority argument is set as appropriate.
audit: "/bin/ps -ef | grep $apiserverbin | grep -v grep"
tests:
test_items:
- flag: "--kubelet-certificate-authority"
set: true
remediation: |
Follow the Kubernetes documentation and setup the TLS connection between the apiserver and kubelets. Then, edit the API server pod specification file
$apiserverconf on the master node and set the --kubelet-certificate-authority parameter to the path to the cert file for the certificate authority.
--kubelet-certificate-authority=<ca-string>
scored: true
Fix all of the following violations that were found against the ETCD:-
a. Ensure that the --auto-tls argument is not set to true
Edit the etcd pod specification file $etcdconf on the master
node and either remove the --auto-tls parameter or set it to false.
--auto-tls=false
b. Ensure that the --peer-auto-tls argument is not set to true
Edit the etcd pod specification file $etcdconf on the master
node and either remove the --peer-auto-tls parameter or set it to false.
--peer-auto-tls=false
SIMULATION
Context
A default-deny NetworkPolicy avoids to accidentally expose a Pod in a namespace that doesn't have any other NetworkPolicy defined.
Task
Create a new default-deny NetworkPolicy named defaultdeny in the namespace testing for all traffic of type Egress.
The new NetworkPolicy must deny all Egress traffic in the namespace testing.
Apply the newly created default-deny NetworkPolicy to all Pods running in namespace testing.
Correct Answer:
See the Explanation below
Explanation:


SIMULATION
Create a User named john, create the CSR Request, fetch the certificate of the user after approving it.
Create a Role name john-role to list secrets, pods in namespace john
Finally, Create a RoleBinding named john-role-binding to attach the newly created role john-role to the user john in the namespace john.
To Verify: Use the kubectl auth CLI command to verify the permissions.
Correct Answer:
See explanation below
Explanation:
se kubectl to create a CSR and approve it.
Get the list of CSRs:
kubectl get csr
Approve the CSR:
kubectl certificate approve myuser
Get the certificate
Retrieve the certificate from the CSR:
kubectl get csr/myuser -o yaml
here are the role and role-binding to give john permission to create NEW_CRD resource:
kubectl apply -f roleBindingJohn.yaml --as=john
rolebinding.rbac.authorization.k8s.io/john_external-rosource-rb created kind: RoleBinding apiVersion: rbac.authorization.k8s.io/v1 metadata:
name: john_crd
namespace: development-john
subjects:
- kind: User
name: john
apiGroup: rbac.authorization.k8s.io
roleRef:
kind: ClusterRole
name: crd-creation
kind: ClusterRole
apiVersion: rbac.authorization.k8s.io/v1
metadata:
name: crd-creation
rules:
- apiGroups: ["kubernetes-client.io/v1"]
resources: ["NEW_CRD"]
verbs: ["create, list, get"]
Viewing page 1 out of 14 pages.
Viewing questions 1-5 out of 66 questions.
I'm a newbie for CKS course, and i passed the exam without any additional exam material, only with this CKS exam dump. It is amazing! Guays, you can rely on it!
 By Chad
CKS exam dump is good for studying. I took my first exam and passed. I am very pleased with this choice.
By Dwight
I love everything about you guys. It is you who can give us an ensured opportunity to pass the CKS exam! Thanks so much!
By Gordon
All credit goes to you guys for creating CKS practice test for us. Thank you so much! It’s really a great opportunity to pass the exam!
By Jeremy
CKS dumps are the best ones on the Internet. I was truly amazed by the quality of CKS dumps when preparing for the CKS Exam. I passed it last week.
By Malcolm
Never sat for such a tough exam like the CKS exam. Couldn't believe it when i got the results and had done well. Prep4King, you just saved me with these Prep4King exam dumps. Thanks so much!
By Hamiltion
Disclaimer Policy: The site does not guarantee the content of the comments. Because of the different time and the changes in the scope of the exam, it can produce different effect. Before you purchase the dump, please carefully read the product introduction from the page. In addition, please be advised the site will not be responsible for the content of the comments and contradictions between users.

Prep4King provides you with the high quality and high pass rate CKS study material to all the candidates. You can practice with CKS test engine and enjoy the simulated test environment. Now, study with our CKS training torrent, you will be confident in the actual test and easily pass.
While, if you fail the test unfortunately, do not worry, we guarantee to give you refund.Kindly please show us your failure certification score report, then we will deal with it and refund you.
Frequently Asked Questions
What's the difference of the three versions of CKS study material?
Online test engine can supports Windows / Mac / Android / iOS, etc., because it is the software based on WEB browser. You can use it on any electronic device and practice with self-paced.
Online Test Engine supports offline practice, while the precondition is that you should run it with the internet at the first time.
Self Test Engine is suitable for windows operating system, running on the Java environment, and can install on multiple computers.
PDF version: can be read under the Adobe reader, or many other free readers, including OpenOffice, Foxit Reader and Google Docs.
I'd like to try before purchase. Can I try the demo questions for free?
Yes, our demo questions are part of the complete CKS exam material, you can free download to have a try
How does your testing engine works?
Once download and installed on your PC, you can practice CKS test questions, review your questions & answers using two different options 'practice exam' and 'virtual exam'.
Virtual Exam - test yourself with exam questions with a time limit.
Practice exam - review exam questions one by one, see correct answers.
How long can I get the CKS products after purchase?
You will receive an email attached with the CKS study material within 5-10 minutes, and then you can instantly download it for study. If you do not get the study material after purchase, please contact us with email immediately.
How often do you release your CKS products updates?
All the products are updated frequently but not on a fixed date. Our professional team pays a great attention to the exam updates and they always upgrade the content accordingly.
What are the Terms and Conditions for Refund? And how to refund?
Yes, you will enjoy one year free update after purchase. If there is any update, our system will automatically send the updated study material to your payment email.
Do you have money back policy? How can I get refund if fail?
Yes. We have the money back guarantee in case of failure by our products. The process of money back is very simple: you just need to show us your failure score report within 60 days from the date of purchase of the exam. We will then verify the authenticity of documents submitted and arrange the refund after receiving the email and confirmation process. The money will be back to your payment account within 7 days.
Over 69729+ Satisfied Customers

Our Clients





Prep4King will provide you with the best valid & training material for you to practice. You can get an good result with the help by our high quality study material.
Contact Us
From Monday to Saturday
Support: Contact now
If you have any question please leave me your email address, we will reply and send email to you in 12 hours.
Copyright © 2026 PREP4KING.COM. All rights reserved. All trademarks are the property of their respective owners and we don't provide actual questions from any vendor. Privacy Policy